Senior Application Security Engineer — building AI-assisted security tooling
Working at KATIM (EDGE Group)
Senior Cybersecurity Engineer
Abu Dhabi, UAE Jan 2025 – Present
I own SSDLC and security tooling at KATIM — the whole thing: program,
tools, rollout, and vulnerability management.
SSDLC & Tooling
Defining the SSDLC, planning the implementation, and getting developers to adopt it.
Picked and integrated the security toolchain — Coverity, Checkmarx, Semgrep, Black Duck SCA — into the Jenkins pipelines and automated the security controls.
Built and maintain the S-SDLC knowledge base: tools, procedures and secure coding guidelines.
Vulnerability Platform
Built a custom vulnerability-management tool that covers roughly 1,000 repositories.
Consolidates six scanners across SAST, SCA and secret scanning, dedupes the findings, and runs AI-assisted triage on a local model for privacy.
CVE Impact Analysis
Built the tool that checks whether a published CVE actually reaches our products by analyzing the build and the code, not just the advisory.
AI in the Security Work
Summarizing pull requests, generating custom security rules, and producing per-repo security profiles tuned to each project's characteristics.
Lead the team's secure AI adoption: evaluating hosted and local models, defining guardrails, and building the knowledge bases they run on.
⇄
Connections
— AppSec · 2025 – Present
— AppSec · 2023 – 25
— Security Delivery · 2020 – 23
— SOC · 2020
— Software Development · 2019
Previously
FNZ · Accenture · Deloitte
Madrid, ES 2020 – 2025
Five years of security work in Madrid before KATIM — from SOC
operations to application security to leading a supply-chain
initiative across an entire organization.
FNZ Group — Application Security Engineer
Oct 2023 – Jan 2025
Built the automated security process in GitHub Actions for FNZ's wealth-platform clients: SAST on every pull request, secret scanning, dependency policy.
Owned AppSec across a portfolio of client platforms — pentest scheduling, security requirements, vendor selection — and led the supply-chain workstream.
Accenture — Senior Application Security Analyst
Oct 2020 – Oct 2023
Led the software supply-chain security initiative across the organization and built its SLSA knowledge base.
Planned and delivered the DevSecOps transition: SAST, SCA, IaC, DAST and container scanning.
Stayed hands-on: threat modeling, NIST and OWASP gap analyses, and security code reviews with custom rulesets per client.
Deloitte — Cybersecurity Operator
Feb – Oct 2020
SOC operations: threat monitoring and incident triage across CrowdStrike, FireEye, Akamai, Splunk and Kibana, plus phishing analysis and end-user support.
⇄
Connections
My Projects
Selected Builds
Side & Work Builds Ongoing
These started as things that annoyed me at work and did not go away
on their own. The loop is the same every time: reproduce the problem,
build the fix, prove it works, then let AI take over the repetitive part.
CVE Impact Analyzer
The problem: a CVE feed says a dependency is vulnerable. It does not say whether our product ever calls the vulnerable code, so engineers either patch everything or guess.
What I built: a tool that reads the advisory, then walks the build process and the source to check whether the affected code is actually reachable from our products.
The outcome: a verdict per CVE, backed by file and line evidence. An engineer can check the reasoning instead of trusting it, and the fix time goes to the CVEs that matter.
AI-Assisted Triage
The problem: six scanners over roughly 1,000 repositories produce more findings than a security team can read, let alone explain to developers.
What I built: the AI layer on top of the vulnerability platform. Triage of new findings, pull-request summaries, generated security rules, and a security profile per repository tuned to what that project actually does.
The outcome: developers get a short verdict and the reason behind it instead of a raw scanner dump. Everything runs on local models, so no source code leaves the building.
Checkmarx FP Dashboard
The problem: engineers mark scanner findings as false positives and the decision disappears into the tool. Nobody checks whether they were right.
What I built: a dashboard that collects those verdicts and has an AI pass review each one against the code it points at.
The outcome: the security program can see which rules produce the most noise and which "not exploitable" marks need a second look, so tuning is driven by data rather than complaints.
Onboarding Assistant
The problem: new engineers on complex projects ask the same questions, and the veterans pay for it in interruptions.
What I built: an assistant over the team's knowledge base, served by a local model.
The outcome: newcomers ask the assistant first, and the internal documentation never leaves the building.
Vulnerability Manager
The problem: most vulnerability managers aggregate reports from scanners you run elsewhere, which means more pipelines to set up and keep in sync.
What I am building: a vulnerability manager with the scanners inside. Semgrep, TruffleHog and Trivy run from the tool itself, with deduplication and triage on top.
Work in progress. The goal is one install that takes a repository to triaged findings.
Bug Bounty Hunter
The problem: bug bounty work is mostly repetition. Reading the scope, mapping the attack surface and running the first checks eat the hours before anything interesting shows up.
What I am building: an agent-driven hunter that takes a program's scope, discovers the targets and runs the recon and first-pass checks, then hands me the leads worth a human look.
Work in progress.
⇄
Connections
— Verdicts With File:Line Evidence
— Local-Model Tooling
— Finding-Review Analytics
— Local-Model Knowledge Base
— Scanners Built In · Work in Progress
— Agent-Driven Recon · Work in Progress
— Six-Scanner Triage Engine
Toolstack
Daily Drivers
In Rotation
AI
Claude and GPT for the engineering work; local models via Ollama where the data can't leave the building; MCP for wiring agents to real tools.
Scanning
Semgrep — with custom rules — plus Coverity, Checkmarx, Black Duck SCA, and Trivy.
Pipelines
Jenkins and GitHub Actions — where the scanners actually live and the controls get enforced.
Glue
Python and Bash for everything in between.
⇄
Connections
— Plus Toolstack
Areas of Interest
Plus Toolstack
Research & Tooling Ongoing
The threads I keep pulling on outside the ticket queue — and the tools I pull them with.
⇄
Connections
— SLSA · Provenance
— Auto-Triage · Rules · Agents
— LLM Apps · Agents · MCP
— Harnesses · Orchestration
— Scanners · Pipelines · AI
Supply-Chain Security
SLSA · Provenance
Initiative Lead → Practitioner 2022 – Present
From leading Accenture's supply-chain initiative — building its SLSA knowledge base — to FNZ's dependency policy to KATIM's SCA rollout: provenance, integrity, and knowing what is actually inside the build.
⇄
Connections
— Plus Toolstack
AI for Security
Auto-Triage · Rules · Agents
Research & Practice 2024 – Present
Using AI to do the security work: auto-triage at platform scale, generated security rules, per-repo risk profiles — and the evals, guardrails and human review that keep the output trustworthy.
⇄
Connections
— Plus Toolstack
— Local-Model Tooling
Securing AI
LLM Apps · Agents · MCP
Research 2024 – Present
The security of AI systems themselves: LLM applications, agents and the tools they reach, MCP threat models, prompt injection — and reviewing machine-written code before it ships.
⇄
Connections
— Plus Toolstack
Agentic Engineering
Harnesses · Orchestration
Practice 2025 – Present
Building with agents, not just about them: harnesses, orchestration across terminals and worktrees, local models doing real work — engineering habits that carry straight back into the security tooling.
⇄
Connections
— Plus Toolstack
— Agent-Driven Recon · Work in Progress
Álvaro De la Torre Ruiz
Senior Application Security Engineer
KATIM (EDGE Group) · Abu Dhabi, UAE 2025 – Present
Six years of application security across healthcare, fintech and
defense. I own the secure SDLC end to end: the CI/CD controls, the
governance and the tools. When the tools available do not fit, I build
them. An AI-assisted vulnerability platform covering 1,000+ repositories
supports the security program, and I’m developing CVELens for firmware CVE analysis.
Six years of application security across healthcare, fintech and defense. I run the SSDLC and build the tools it needs.
Álvaro De la Torre
Senior Application Security Engineer · Dubai
I build security tools and run the AppSec programs they support. Currently at KATIM, working on AI-assisted triage and CVE analysis.
Experience
Software development, security operations, then application security. Here's where I've worked.
KATIM (EDGE Group)Jan 2025 to presentSenior Cybersecurity Engineer+
I run the secure development program and build security tooling at KATIM.
Abu Dhabi, UAE
Defining the SSDLC, planning the implementation, and getting devs to adopt it
Picked and integrated the security toolchain (Coverity, Checkmarx, Semgrep, Black Duck SCA) into our Jenkins pipelines and automated the security controls
Built a custom vulnerability-management tool that covers ~1,000 repos, consolidates 6 scanners across SAST, SCA, and secret scanning, dedupes findings, and runs AI-assisted triage on a local model for privacy
Integrating AI elsewhere in our security work: summarizing PRs, generating custom security rules, and producing per-repo security profiles tuned to each project's characteristics
FNZ GroupOct 2023 to Jan 2025Application Security Engineer+
I built security checks into GitHub Actions for FNZ's wealth-platform clients and led the supply-chain workstream.
Madrid, ES
Led the supply-chain security workstream
GitHub Actions checks: SAST on every PR, secret scanning, dependency policy
Owned AppSec across a portfolio of client platforms (pentest scheduling, security requirements, vendor selection, reporting back to stakeholders)
Analyzed vulnerabilities so business owners could see the risk and prioritize what to fix
AccentureOct 2020 to Oct 2023Senior Application Security Analyst+
I led the software supply-chain security initiative and worked on the DevSecOps transition.
Madrid, ES
Planned and delivered the DevSecOps transition: SAST, SCA, IaC, DAST and container scanning
Built up the supply-chain knowledge base, focused on SLSA
Stayed hands-on: NIST/OWASP gap analyses, threat modeling, and security code reviews with Fortify, Sonarqube, and Semgrep (custom rules per client when it helped)
Deloitte EspañaFeb 2020 to Oct 2020Cybersecurity Operator+
I worked in security operations, monitoring threats and triaging incidents.
Madrid, ES
OrangeFeb 2019 to Nov 2019Software Developer Intern+
I started as a software developer intern at Orange.
Madrid, ES
Does this CVE affect our firmware?
CVELens · Under active development
A vulnerable package version is only part of the story. I built CVELens to check a CVE against a specific Yocto firmware build, including the packages it ships, applied patches, and whether the affected code can be reached.
Establish what shipped. Read the build's package scan and image manifest, then fetch the matching source revisions.
Check the advisory against the code. Combine build checks with a local model that reviews patches, reachability, and attacker-controlled input.
Leave a reviewable decision. Return a verdict with code references, citations, and unanswered questions. Missing evidence stays visible.
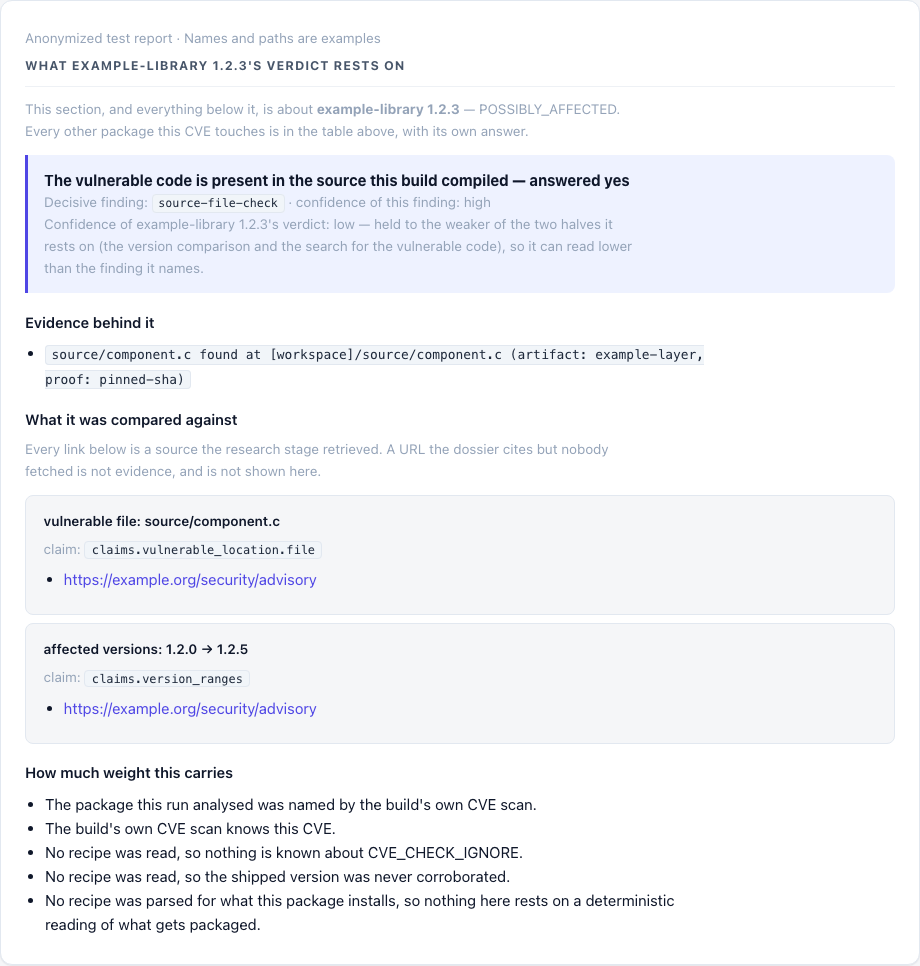
Anonymized report from a test fixture. Names and paths are examples; build inputs, advisory responses, and model responses are simulated.
This test finds the vulnerable file and returns POSSIBLY_AFFECTED. It demonstrates the report format, not a confirmed vulnerability in a real product.
The engineer still makes the call
Source-code review runs on a local model. A second review pass checks for gaps, and the report keeps the evidence behind each verdict. I’m still developing the tool; its verdicts need human review.